How To Break XML Encryption - Automatically
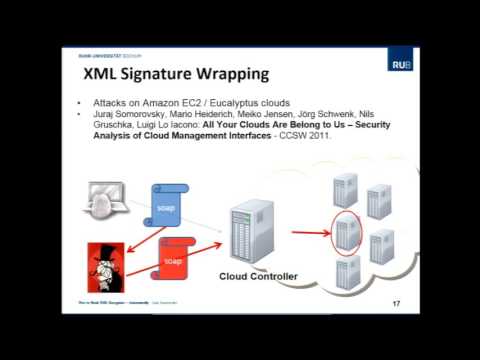
summary
Automatic adaptive chosen-ciphertext attacks decrypt XML-encrypted messages and recover session keys by abusing parsers and error responses, implemented as a WS-Attacker plugin that automates detection, oracle mapping and exploitation. Symmetric CBC attacks recover one plaintext byte with 14 server queries per plaintext byte; RSA-style attacks take ~400,000+ server queries to expose session keys. The tool finds real flaws: four of five tested defaults are exploitable, including Apache CXF and IBM DataPower.
AI-written summary · about
chapters (13)
- 0:00Intro
- 0:40About me
- 1:21Presentation
- 5:03The Problem
- 9:16Hybrid Encryption
- 12:42Symmetric Encryption
- 14:57Plain Text Validation
- 16:02Flipping ASCII
- 19:04What could go wrong
- 21:31How to analyze this automatically
- 32:49Secure Cryptography
- 34:12Conclusion
- 35:38Questions
related talks
 54mBroken Crypto is Broken
 42mBreak Crypto like a Pro!
 54mYes, you too can break crypto Exploiting common crypto mistakes
 34mHacking the Oracle Application Framework
 39mWhat You Didn't Know About XML External Entities Attacks
 56mAttacking AI
 51mMaking the most of Security Tests
 58mModern web application bugs