Server Tailgating - A Chosen-PlainText Attack on RDP
summary
Demonstrates a chosen-plaintext attack against Microsoft Remote Desktop Protocol (RDP) that exploits a logical vulnerability in a common Windows authentication protocol. Explains how an attacker can craft plaintext inputs to subvert Windows authentication mechanisms and compromise network logins.
AI-written summary · about
chapters (29)
- 0:00Intro
- 1:29black hat What We Will Show
- 2:44blackhat Kerberos
- 4:26black hat MSRPC - Microsoft Remote Procedure Call
- 5:14black hat GSSAPI / SSPI
- 6:29black hat TLS (Transport Layer Security)
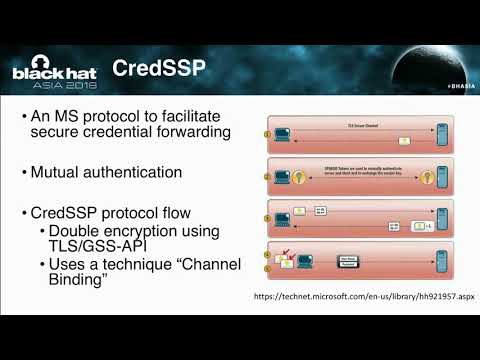
- 7:12black hat CredSSP
- 9:19black hat RDP (Remote Desktop Protocol)
- 10:43black hat RDP Flow
- 11:41black hat RDP - Certificate Validation
- 12:34blackhat Protocols Recap
- 13:16black hat The Journey
- 15:16black hat Do You See the issue?
- 15:59blackhat Vulnerability Flow Chart
- 17:47black hat RSA Quick Overview
- 19:16blackhat "Broken" RSA
- 21:05blackhat Requirement For Public Key
- 21:53black hat Finding A Suitable Protocol
- 22:39black hat MSRPC!
- 23:04blackhat #1 Try - Exploiting NTLM
- 24:26blackhat #2 Try - Exploiting Kerberos
- 25:04black hat Exploit Details
- 26:18black hat Success!
- 31:26black hat Should I care?
- 32:31black hat Affected Systems
- 33:10black hat Patch Details
- 35:37black hat Disclosure Timeline
- 37:08black hat Tools
- 37:24blackhat Key Takeaways
related talks
 49mHe Said, She Said – Poisoned RDP Offense and Defense
 39mI Watched You Roll the Die: Unparalleled RDP Monitoring Reveal Attackers' Tradecraft
 39mFuzzing and Exploiting Virtual Channels in Microsoft Remote Desktop Protocol for Fun and Profit
 43mHuman Involvement Behind Remote Desktop Protocol Brute-Force Attacks
 47mFinding a Needle in an Encrypted Haystack
 40mFighting Where They Aren't: How Attackers Avoid Endpoints in Modern Attacks
 48mA Practical Attack Against VDI Solutions
 48mHacking Exposed: Next-Generation Tactics, Techniques, and Procedures