Exploiting Social Navigation
summary
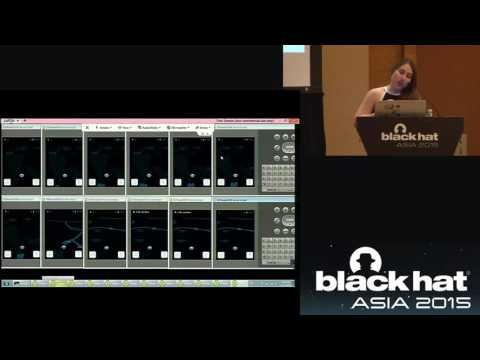
Researchers create armies of fake Waze clients using Android emulators and ADB, set fake GPS reports, and program realistic stop-and-go movement to generate false congestion that changes routing; they also capture screenshots, use OCR template-matching to extract usernames and timestamps, and link them to locations to enable continuous tracking. Experiments run ~15 emulators per machine, scale to thousands of users, successfully redirect routes and map real user paths, and prompt partial server-side mitigations from the vendor.
AI-written summary · about
chapters (7)
- 0:00Start
- 0:15Outline
- 3:14Motivation
- 12:40Spoof Attack: Implications
- 14:18Attack #2: Tracking Users
- 22:10Mitigating Attacks
- 22:51Summary
related talks
 25mAll Your GPS Are Belong To Us: Towards Stealthy Manipulation of Road Navigation Systems
 17mSidewinder Targeted Attack Against Android in the Golden Age of Ad Libs
 45mI just hacked your app!
 07mI just hacked your app!
 36mI just hacked your app!
 30mReversing Mobile Malware
 42mThe Ways Hackers Are Taking To Win The Mobile Malware Battle
 20mExploring Android Accessibility Malware