HTML5 JS Security
summary
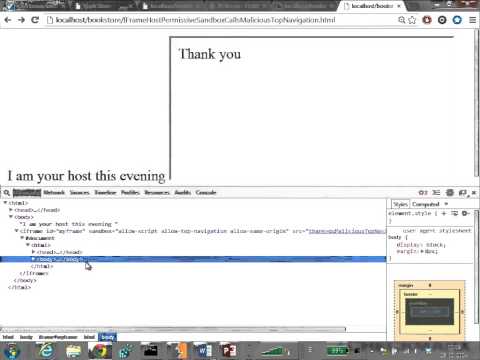
Shows concrete exploits and demos: uses html2canvas screenshots to capture same‑origin iframe content and a patched routine that modified input type reveals passwords during render, demonstrates WebSocket‑based internal network scanning and sandbox pitfalls where allowing sameOrigin+scripts lets the child DOM add allowTopNavigation but browsers differ (Chrome blocks script‑added navigation while Firefox and IE may not), modifies game logic via Burp live JS tampering to double scores, and reports the camera/mic/geolocation capture and the demo success rate roughly 25 percent.
AI-written summary · about
chapters (5)
related talks
 34mJS Security - A Pentesters Perspective
 51mHTML5: Risky Business or Hidden Security Tool Chest?
 40mHostile JavaScript: Attacking and Defending the Browser
 23mJavaScript attack surface
 21mCreepy frontend mistakes
 33mHacking The Front-End
 32mWriting Secure JavaScript Code
 32mJavaScript security: a retrospective