Implementing an OAuth 2 authorization server with Spring Security - the new way!
summary
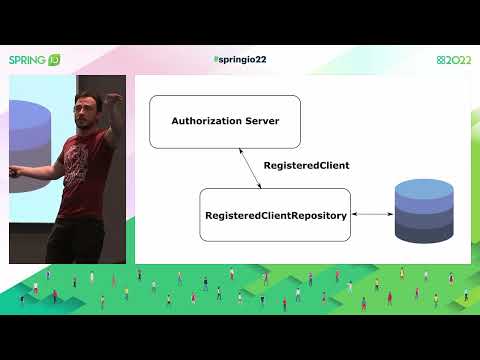
Builds a working authorization server with Spring Security Authorization Server v0.3.0, using an in-memory RegisteredClientRepository and UserDetailsService, ProviderSettings, and an RSA keypair JWK source. Demonstrates the authorization code with PKCE flow end-to-end: browser login returns a code, exchange at the token endpoint returns an access token and an ID token (no refresh token in this demo). Tokens are JWT signed with generated RSA key (kid matches JWKS endpoint). Notes: declared production since 0.2.0 but pre-1.0, expect possible breaking changes.
AI-written summary · about
chapters (8)
- 0:00Start
- 11:10Add the Dependency from Maven
- 11:43Configuration Classes
- 13:16Password Encoder
- 14:14Security Filter Chain
- 15:11Client Credentials
- 19:23Provider Settings Builder Build
- 39:18Token Settings
related talks
 51mEnterprise Security with Spring Authorization Server 1.0
 01h 02mGetting Started with Spring Authorization Server
 48mThe new Spring Security
 51mEverything new in Spring Security 6 baked with a Spring Boot 3 recipe
 50mOAuth2 protocol
 56mSecured REST Microservices with Spring Cloud
 46mOAuth for Java Developers
 01h 26mSecuring Rest-ful Web Services with OAuth2