Multi-Cluster & Multi-Cloud Service Mesh with CNCF’s Kuma and Envoy

summary
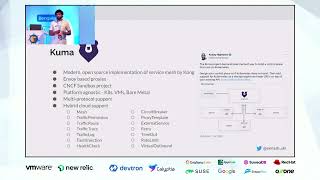
Kuma deploys an Envoy-based data plane across GKE and EC2 VMs with a global/remote control plane that auto-syncs policies and ingress for cross-zone connectivity. The demo runs GKE east/west plus an EC2 zone, enables one-click mTLS with a built-in CA and daily proxy cert rotation, and requires explicit TrafficPermission ACLs. TrafficRoute rules split weights across clouds and zones; observability exports to Zipkin/Jaeger/Splunk and Grafana. Kuma 1.0 is released and supports multi-zone hybrid clusters.
AI-written summary · about
chapters (16)
- 0:00Introduction
- 3:15Use Cases
- 4:07Kuma Overview
- 4:26Kuma Features
- 5:11Why Service Mesh
- 5:29Envoy
- 5:57Why Kuma
- 6:22Deploying Kuma
- 7:37Kuma GUI
- 8:02Service Mesh for Kubernetes
- 8:38Gateway Integration
- 10:21Frontend Integration
- 10:45Global Control Plane
- 11:39GUI Overview
- 13:01Enabling Zero Trust Security
- 19:14Release
related talks
 10mLightning Talk
 04mWhat’s New in Kuma: Advanced Service Mesh Capabilities
 15mKeynote: Deploying an Envoy-Based Service Mesh in Minutes Across Kubernetes and VMs
 20mKong Meetup: Kuma the Universal Service Mesh
 29mZero Trust Security with Service Mesh
 50mMulti-Cluster Kubernetes and Service Mesh Patterns
 42mSIG Multi-Cluster Deep Dive
 31mAn Adventure in Multi Cloud with Kubernetes and Distributed Data