The DROWN Attack
summary
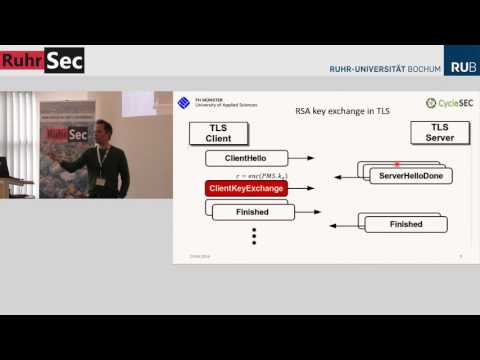
A cross‑protocol exploit uses an SSLv2 server as a Bleichenbacher RSA padding oracle to decrypt recorded TLS 1.2 sessions using 2048‑bit RSA, implemented to recover a session in under 8 hours on Amazon EC2 for $440. Internet scans find 33% of HTTPS servers (22% with browser‑trusted certs) exposed due to key/certificate reuse. Attack needs roughly 1,000 observed TLS handshakes, ~40,000 SSLv2 handshakes and ≈2^50 brute‑force work unless GPU/FPGA/OpenSSL implementation flaws reduce it to minutes.
AI-written summary · about
chapters (11)
- 0:00Introduction
- 0:45SSL v2
- 3:13SSL v2 support
- 11:41Premaster secret
- 15:22Padding Oracle
- 18:41Export ciphers
- 21:02We dont yet know
- 25:52Complexity
- 27:25Shared keys
- 34:30OpenSSL
- 37:25BruteForce
related talks
 25mDROWN: Breaking TLS Using SSLv2
 51mA Retrospective on the Use of Export Cryptography
 49mBar-Mitzva Attack: Breaking SSL with 13-Year Old RC4 Weakness
 44mCryptography in the age of Heartbleed
 55mUnlocking The Secrets Of TLS
 24mReturn Of Bleichenbacher’s Oracle Threat (ROBOT)
 53mThe BEAST Wins Again: Why TLS Keeps Failing to Protect HTTP
 01h 26mTLS Cryptography for Programmers