Five Key Trends In Application Security
summary
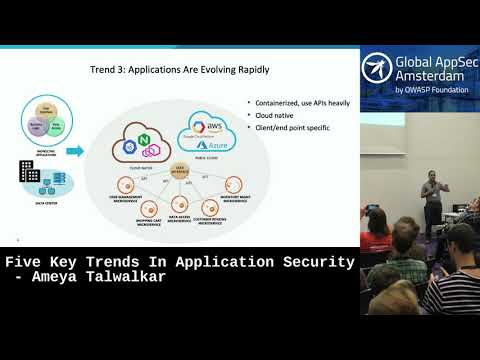
Five concrete trends and why they matter: apps move across data centers public and private clouds, perimeter shifts to CDNs and often fragments across multiple CDN vendors; monoliths split into hundreds of externally exposed APIs and microservices; regulation risk rises under GDPR and CCPA when vendors inspect traffic; automated attacks explode — 14 billion leaked credentials, 0.1–0.5% credential stuffing success rates, commodity tools like Sentry MBA with configs sold for $5–$500, and “bulletproof proxies” renting millions of IPs. Recommended fixes: security that moves with apps, API coverage, vendor compliance proof, visibility without heavy instrumentation, and open integrations.
AI-written summary · about
chapters (23)
- 0:00Introduction
- 1:15About Ameya
- 1:56Trends Overview
- 2:35Trend 1 Journey to the Cloud
- 4:49Trend 2 Multiple CDNs
- 6:27Trend 3 Proliferation of APIs
- 7:33Trend 4 Compliance
- 9:05Trend 5 Attack Surface
- 12:27Credentials
- 12:42Recent Breaches
- 13:19Industry
- 13:47Tools
- 15:01Behavior
- 15:28Nike Bot
- 16:41Cybercriminal Infrastructure
- 17:34Residential IP addresses
- 19:10Geo distribution
- 21:15Mobile apps
- 21:55Account takeover
- 23:42Fake account creation
- 24:58Content scraping
- 27:39Recommendations
- 31:36Questions
related talks
 23mCloud Security Megatrends - No Data-Driven Innovation without Security
 24mSecurity in 2023 and Beyond: Automation, Analytics and Architecture
 47mThe Megatrends Driving Cloud Adoption – and Improving Security – for All
 01h 03mTen Key Steps for Enhanced Web App Security
 48mHow to Meet the New Mobile Application Security Imperative
 50mThe Application Security State of the Union
 17mThe Future of Cloud-Native Security
 24mSecuring the Modern API Ecosystem