Seeing Through the Fog - Navigating the Security Landscape of a Cloud-First World

summary
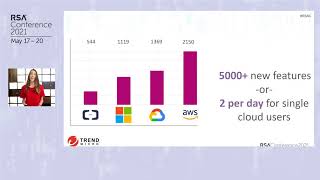
Cloud providers keep the hardware and uptime while enterprises keep the data and misconfigurations cause most damage: public AWS S3 buckets routinely expose terabytes, logging often defaults off or keeps only 14 days of events, and departments spin up Slack/Office365/Dropbox accounts outside IT. Main failures are a huge skills gap plus identity sprawl and privilege creep; detection rules “deploy and decay” without tuning. Practical fixes: inventory and audit, shift to automated provisioning and enforcement, and prioritize auth, authorization and accounting.
AI-written summary · about
chapters (23)
- 0:00Intro
- 1:36Reflection Time
- 2:15Digital Transformation
- 2:57What is the Cloud
- 3:26IT vs Security
- 4:01Race to the Cloud
- 5:01Data Breach Bubbles
- 5:21S3 Buckets
- 5:33Deloitte
- 5:54Breach Fatigue
- 6:31Causation
- 6:54Provider vs Enterprise
- 8:42Lack of Understanding
- 9:51Operator Responsibility
- 10:17Skills Gap
- 11:38Whos Responsible
- 12:39SAS
- 13:37Cloud Security
- 14:26Get Better
- 19:11Triple A
- 21:35Technical Challenges
- 21:45Keynote
- 30:10Business Unit Leaders
related talks
 26mCloud Security Lessons
 45mProtecting you from you: Misconfiguration-caused breaches
 57mCloud’s Dirty Little Secret: It Was Misconfigs All Along
 43mWalking on Broken Clouds
 31mCloud Threat Landscape - 2021
 39mPerils of the cloud
 40mWork Smarter Not Harder: Tips to Approach Cloud Security the Easier Way
 51mCloudSec Hero to Zero: Self-Obsolescing Through Prolific Efficiency