Redefining Threat Modeling: Security team goes on vacation

summary
Claims that a structured program trains engineers to own most threat models using STRIDE and three staged workshops, then phases of observation, review and a security‑optional state. Implementation ships training slides on GitHub, reaches about 80 of 150–200 engineers in a year, and engineers find roughly 90% of critical/high issues. Notes that it increases threat‑model frequency, lowers security bottlenecks, but requires multi‑year commitment and continuity.
AI-written summary · about
chapters (10)
- 0:00Intro
- 0:50AGENDA
- 10:03HOW DOES IT SOLVE OUR PROBLEMS?
- 10:46WHAT IS SELF-SERVE THREAT MODELING?
- 12:17SELF-SERVE PHASES
- 16:48TRAINING NOTES
- 18:33OBSERVATION PHASE (TRAINING v2)
- 19:56OBSERVATION NOTES
- 24:32SELF-SERVE WINS
- 27:53LINKS FOR SELF-SERVE
related talks
 48mRedefining Threat Modeling: Security Team Goes on Vacation
 52mLessons From The Threat Modeling Trenches
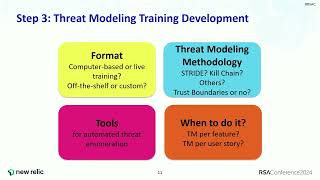 48mTeaching Software Engineers to Threat Model: We Did It, and So Can You
 39mValue driven threat modelling - security by design
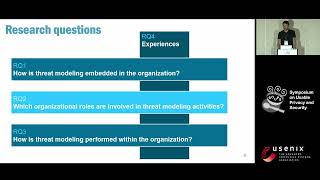 11mThreat modeling state of practice in Dutch organizations
 53mThreat Modeling: uncover vulnerabilities without looking at code
 22mEmpowering Developers through Threat Modeling Excellence
 58mThreat Modeling In And For Your Organization