Lattice-Based Post-Quantum iO from Circular Security with Random Opening Assumption

summary
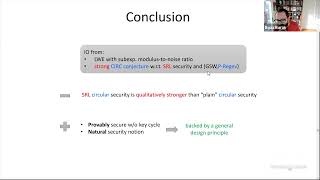
Presents a concrete construction of lattice-based post-quantum xiO that reduces to a new assumption called Circular Security with Random Opening and specifies why the hint is marginally uniform and leaks no decryption noise. Uses Regev/GSW-style FHE, dual GSW encodings, rerandomization and CRS programming to produce succinct openings (square-root compression of the truth table) and shows the scheme avoids known LWE-with-hint attacks while leaving security tied to the CRO pseudorandomness target.
AI-written summary · about
chapters (11)
- 0:00Motivation for post-quantum IO
- 3:16The importance of heuristics
- 5:34Constructing IO from LWE
- 10:08Framework for succinct IO
- 13:48Previous works and vulnerabilities
- 17:35Circular security with random opening
- 20:44Defining the CRO assumption
- 27:30GSW homomorphism and sampling
- 39:27Building xiO with magic encryption
- 45:50Achieving independence in evaluation
- 53:35CRS programming and conclusion