How Things Are Going For APT41 In 2024
summary
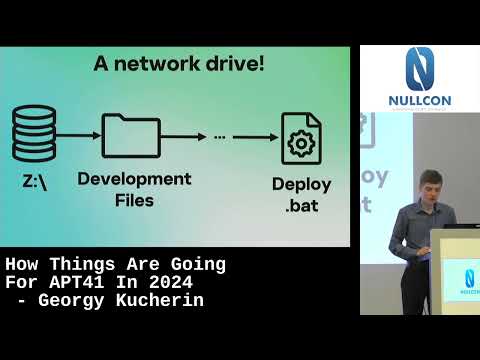
APT41 compromises a South Korean game developer in Jan 2024 by escalating from a low-privilege account to modify a writable shared network drive deployment script, planting an MSI that drops a DLL loader hidden in the zone.identifier NTFS stream. Persistence uses COM object redirection plus a scheduled task to evade scanners, the loader holds an RC6-encrypted loader that yields a backdoor speaking HTTPS with DNS fallback via 8.8.8.8, and operators later run Cobalt Strike and open-source post-exploitation tools.
AI-written summary · about
chapters (18)
- 0:00Introduction
- 0:29Advanced Persistent Threats
- 1:55What is APT41
- 6:24Initial infection
- 7:21Lateral movement
- 8:30Network drives
- 9:38Batch file
- 10:22MSI file
- 10:57Com objects
- 11:42Home hijacking
- 16:01NTFS File Stream
- 17:41PE File
- 18:04decryption tool
- 19:07Backdoor
- 20:39Commands
- 21:45Open Source Tools
- 23:01Backdoor Origins
- 24:06PTB Pass
related talks
 32mOperation Clairvoyance: How APT Groups Spy on the Media Industry
 38mClose Encounters of the Advanced Persistent Kind: Leveraging Rootkits for Post-Exploitation
 40mBeyond Living-Off-the-Land: Why XP Exploits Still Matter
 44mAnatomy and Defense of LOTL Fileless Intrusions
 55mRevealing the Attack Operations Targeting Japan
 52mStart covering your bases & Stop chasing APT headlines
 31mThe Wolves Among Us… A Tale of APT’s Thievery
 40mLearning from the Enemy: A Look Inside the Techniques of Ocean Lotus /APT32