Deobfuscate UEFI/BIOS Malware And Virtualized Packers
summary
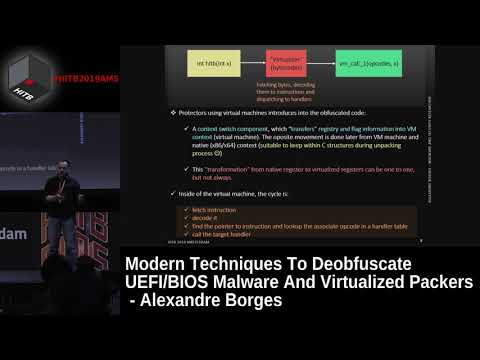
Shows concrete deobfuscation steps: use Metasm and Miasm to backtrace virtualized handlers and collapse dozens of VM-translated instructions into original x86 operations (example reduces a transformed sequence back to EAX = EAX + ECX). Demonstrates emulation with Capstone/Keystone/Unicorn and symbolic execution to recover semantics, plus live techniques for infected MBR/UEFI analysis using IDA Pro attached to a VM via GDB. Details SPI flash dumping, SMM/BootGuard attack surfaces and where secure boot or VSM fail.
AI-written summary · about
chapters (10)
- 0:00Introduction
- 1:03Malware obfuscation techniques
- 3:02Analyzing protected code
- 9:59Code analysis frameworks
- 16:04Disassembly and back-tracing
- 22:18Emulation and symbolic analysis
- 30:32Windows security and bootkits
- 37:28Boot process and MBR attacks
- 52:16UEFI and firmware security
- 1:00:57Firmware protection and conclusion
related talks
 45m"Advanced Malware Threat: handling obfuscated code using..."
 01h 04mAnalyzing UEFI BIOSes from Attacker & Defender Viewpoints
 49mBreaking Hardware-Enforced Security With Hypervisors
 47mExposing Bootkits with BIOS Emulation
 51mFull System Emulation: Achieving Successful Automated Dynamic Analysis of Evasive Malware
 49mBreaking Through Another Side: Bypassing Firmware Security Boundaries from Embedded Controller
 50mMTV Reboot — my Super Sweet 16-bit malware...
 57mExtreme Privilege Escalation on Windows 8/UEFI Systems