Simplifying Secrets Management in the Public Cloud
summary
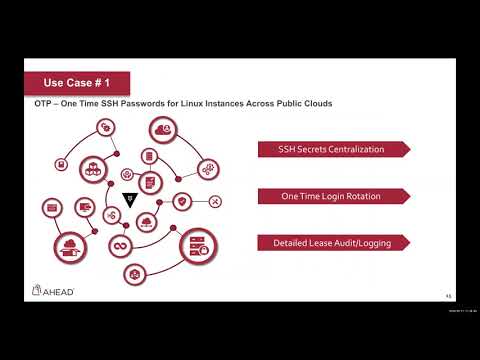
Shows Vault centralizing secrets across clouds with live demos that work: an SSH one-time passwords flow using the SSH secrets engine, an AWS secrets engine issuing dynamic AWS IAM credentials that start/stop tagged EC2 instances, and database credential rotation for SQL Server and Azure RDS with auto-generated users and passwords. Setup is simple: enable engines, create roles and policies, install an SSH helper or run Vault CLI calls. All demos run end-to-end and produce auditable, short-lived credentials.
AI-written summary · about
chapters (4)
related talks
 47mManaging your Secrets in a Cloud Environment
 29mIntro to secrets management using Vault
 22mSecuring AWS Accounts With HashiCorp Vault
 38mKeeping Secrets - A Practical Approach to Managing Credentials
 41mModern Security with Microservices and the Cloud
 29mManaging Secrets in Your Cloud Environment
 31mSecure Your Multi-Cloud Delivery Pipeline with HashiCorp Vault
 29mHow to get dynamic with secrets management