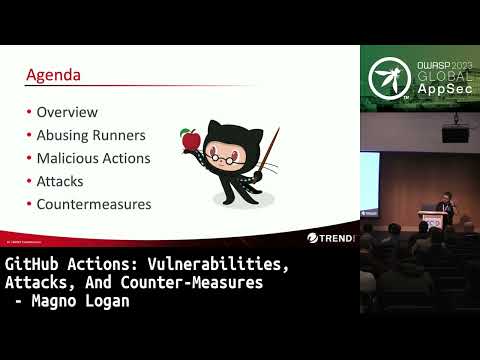
GitHub Actions: Vulnerabilities, Attacks, And Counter-Measures
summary
Shows concrete exploitation: attackers upload actions that run XMrig and mine on Azure VMs, abuse Windows Linux and Mac runners, and automate forked pull requests to inject payloads; finds about 17,000 marketplace actions as dependency surface, VM jobs run up to 72 hours and steps up to six hours, examples use checkout@v2 and third‑party actions, demonstrates a reverse shell to AWS from a runner and stolen GitHub tokens, and notes GitHub changing default token perms to read‑only as a mitigation.
AI-written summary · about
chapters (7)
- 0:00Introduction
- 7:49GitHub Actions overview & setup
- 25:53Vulnerabilities in Actions
- 30:26Abusing runners for crypto mining
- 37:36Malicious marketplace actions
- 45:05Countermeasures & best practices
- 53:25Q&A
related talks
 57mGitHub Actions: Vulnerabilities, Attacks, and Counter-measures
 23mBreaking the Build: How Attackers Abuse GitHub Actions
 32mHacker Traction Through GitHub Actions: Is Your (Open Source) Project Safe?
 55mBeyond the Commit: Weaponizing and Hardening GitHub Actions
 54mAbusing GitHub for fun and profit: Actions and Codespaces Security
 17mIs My (Open Source) Project Safe?
 36mGithub Actions Security Landscape
 15mGitHub Actions: a time bomb for supply chain security