Authentication and Authorization in GraphQL

summary
Shows concrete patterns: extract JWT from headers, verify and attach a context object with user to every resolver; use a reusable checkRole wrapper that throws Apollo's AuthenticationError or ForbiddenError; delegate authorization into model functions or existing REST APIs by passing the request through; implement field- or type-level rules with custom directives; monitor and cache queries with Apollo Engine; prototype running GraphQL on the edge using Cloudflare Workers to cache full query responses for large-scale, high-latency users.
AI-written summary · about
chapters (7)
- 0:00Introduction and speaker intro
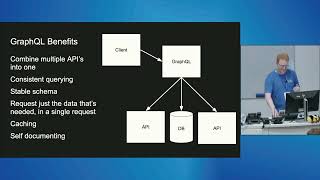
- 3:11GraphQL overview and benefits
- 17:42Authentication and authorization basics
- 27:43Authorization in resolvers and models
- 31:42Custom directives and external authorization
- 34:33GraphQL for next billion users
- 38:11Q&A session
related talks
 51mAPI Security: Securing GraphQL without going around in circles
 29mKeeping Agents in Check: Apollo MCP Authentication
 27mAuthorization in the GraphQL era
 27mDesigning Secure GraphQL APIs : Not a Paradigm Shift but Handling Complexity
 20mAdvanced GraphQL Security with AI-Driven Threat Detection
 21mGraphQL Authorization with Open Policy Agent
 23mAuthorization in GraphQL: Peanut Butter and Chocolate
 28mCurious Use Cases of GraphQL