Cookie Crumbles: Unveiling Web Session Integrity Vulnerabilities
summary
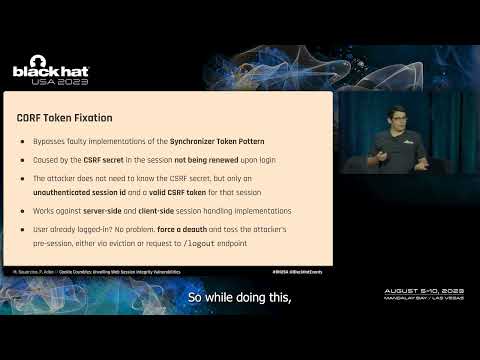
Demonstrates concrete attacks that bypass cookie integrity: a nameless-cookie serialization collision lets a subdomain set cookies that impersonate host‑prefixed or Strict‑Secure cookies; a token‑fixation on synchronizer tokens breaks CSRF protections by reusing pre‑login secrets. Researchers build browser and server differential testers, scan 13 popular frameworks (9 vulnerable) and ~1,500 real subdomains, uncover Firefox document.cookie desynchronization and immutable JS cookies, and show evictions and domain/path quirks enabling session fixation and CORF — many exploits work end‑to‑end and some vendors later patch.
AI-written summary · about
chapters (13)
- 0:00Introduction
- 0:51Who am I
- 1:46What are cookies
- 4:26Threat models
- 5:52Cross origin
- 13:02How we approach the problem
- 13:24Browser testing
- 14:19Strict Secure
- 15:54Cookie headers
- 17:07Valid cookie headers
- 23:14Firefox
- 24:45Document Cookie
- 25:52Conclusion
related talks
 49mCookie Security Myths and Misconceptions
 21mDeath to Cookies
 29mDon't Trust, Verify! - How I Found a CSRF Bug Hiding...
 50mSecure Authentication and Session Management
 43mIf you Give a Hacker a Cookie
 33mHacking The Front-End
 44mCache Me If You Can: Messing with Web Caching
 27mWho Left Open the Cookie Jar? A Comprehensive Evaluation of Third-Party Cookie Policies