Multivariate Solutions To Emerging Passive DNS Challenges
summary
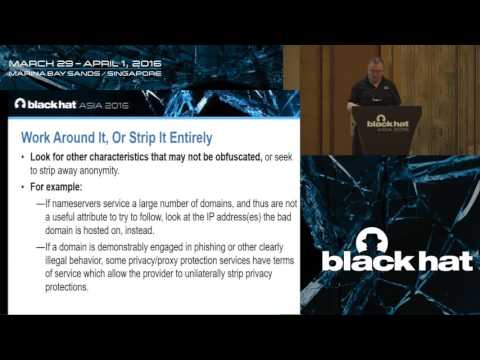
Shows that passive DNS still works when combined with other signals: use passive DNS history to find pre-proxy IPs (example: pillsToronto.net with records back to 2010), pivot from web records to MX/TXT/SPF pivot to identify unique mailservers, run JSON output through JQ and a small Perl “second-level domain” script using the public suffix list, intersect large sets to cut 10M candidates to ~10k then to 39, and finally block recurrences with rpz DNS firewall.
AI-written summary · about
chapters (19)
- 0:00Intro
- 0:53Examples
- 1:43The Attacker
- 3:09The Most Unique Search
- 8:20Who Is
- 12:01Reverse Proxy
- 17:48Example
- 27:30Public Suffix List
- 29:53Domain Big Data
- 31:01Controlled Substances
- 32:28Spam
- 34:20Helios
- 36:29Related Sites
- 37:29IP Address List
- 39:57Data Science
- 47:56Recursive Server
- 49:50Surveillance Capitalism
- 50:37Apple Pie
- 50:56Questions
related talks
 34mUsing DNS as a layer of defense
 01h 27mDNS at 30
 26mMisuse of DNS, the Second Most Used Protocol
 25mDark Side of the DNS Force
 10mAvoiding DNS Pain
 43mBlock DNS exfiltration with dnsmasq proxy
 31mNew Techniques for Split-Second DNS Rebinding
 34mPractical Steps for Reducing Exposure and Detecting Compromise